State of Cloud Security | Datadog
State of Cloud Security

/ / / / / / /

Updated November 2026

This research builds on the previous edition of this article, which was published in October 2025. You can click here to download the graphs for each fact.

The past few months of 2026 have clearly illustrated how profoundly AI is reshaping security, for attackers and defenders alike. But while it is tempting to think that this wave consists of entirely new, AI-specific attacks such as prompt injection or model poisoning, the reality is that AI-assisted development and autonomous agents are amplifying familiar cloud risks and turning vulnerabilities, misconfigurations, and weak identity controls into exposure at unprecedented speed and scale. The fastest-growing risks are in the infrastructure that AI runs on and, increasingly, the infrastructure that AI systems themselves build. In other words, AI is changing the speed and scale of cloud security, but not its fundamentals.

For the 2026 edition of our State of Cloud Security study, we analyzed security posture data from a sample of thousands of organizations that use AWS, Microsoft Azure, or Google Cloud. Our data confirms that the recent rise in reported vulnerabilities does translate to increased real-world risk. We also found that the rapid adoption of cloud-hosted AI services reinforces the importance of cloud security principles, especially when considering new classes of long-lived credentials such as Amazon Bedrock API keys and Gemini API keys. More organizations now rely on SSO for human access and keyless authentication for CI/CD pipelines, yet long-lived cloud credentials remain widespread, stale, and even more dangerous in an agentic age.

Both human and nonhuman attackers are already taking advantage of these gaps. Autonomous agents can now chain a series of ordinary cloud weaknesses (e.g., exposed metadata, over-broad credentials, long-lived secrets) into multi-day intrusions against major platforms’ production infrastructure. Centralized data perimeters and dependency cooldowns are important guardrails, but defense in depth is the only way to consistently enforce comprehensive protection.


Fact 1

Vulnerabilities in cloud workloads have increased fourfold in under a year

Since May 2026, the tech industry has seen the acceleration of what has become known as the Vulnpocalypse: an enormous increase in the volume of vulnerabilities being reported by security researchers and vendors, caused by the advent of security-capable AI models such as Claude Mythos, GLM-5.2, or Kimi K3. Malicious actors have an unprecedented opportunity to compromise applications, and by extension cloud environments. Google Cloud estimates that in the first half of 2026, 44.5% of cloud incidents originated from an attacker exploiting a software vulnerability.

This year, we analyzed vulnerability data from thousands of real-world applications running in AWS, Azure and Google Cloud. We found that this increasing number of vulnerabilities is translating into increased risk. Namely, while a cloud service had a median of 4 high or critical vulnerabilities in February 2026, it had 4x this number 9 months later in November 2026.
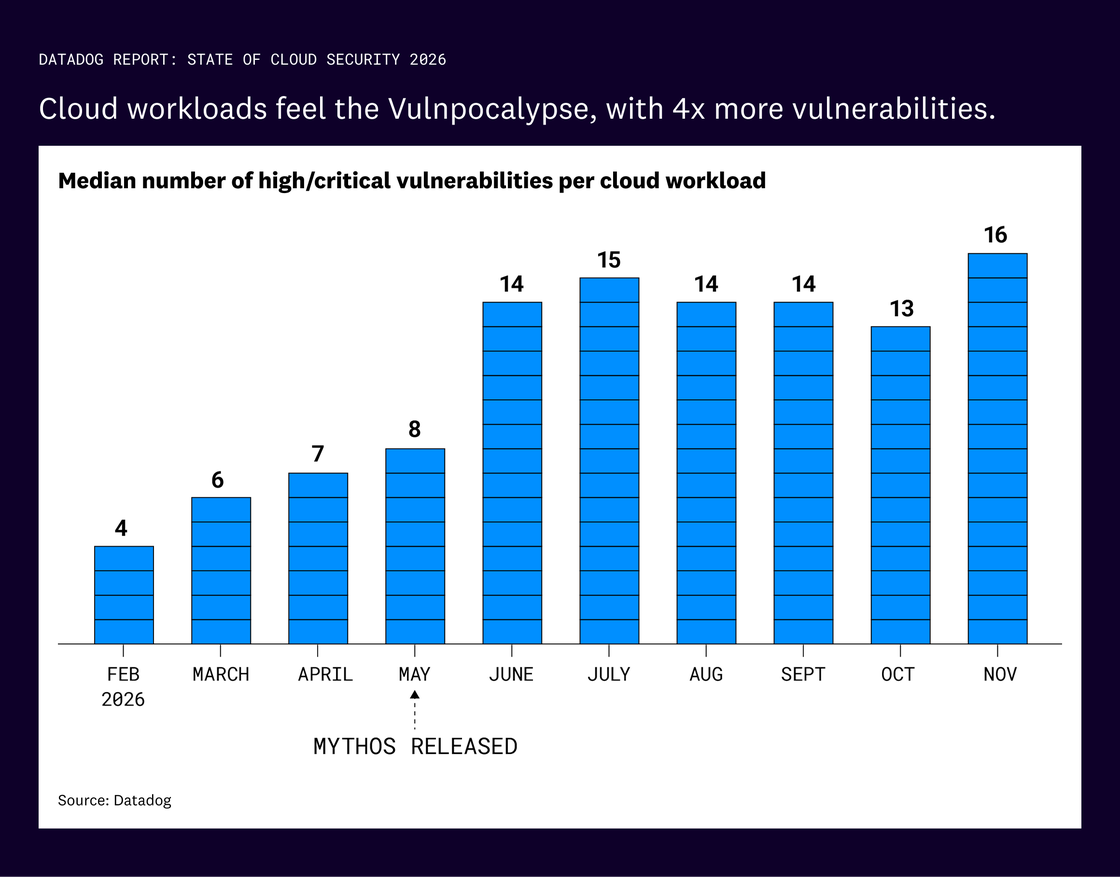
Bar chart titled Median number of high/critical vulnerabilities per cloud workload. Shows the median number of high or critical vulnerabilities per cloud workload rising from 4 in February 2026 to 16 in November 2026, with a sharp jump after Mythos was released in May. Above the chart, a headline reads Cloud workloads feel the Vulnpocalypse, with 4x more vulnerabilities.

This data reveals that the increased number of vulnerabilities in the CVE database isn’t a theoretical risk: it affects an increasing number of real-world applications running in cloud environments, reinforcing the need for cloud security foundations that limit the blast radius of compromised applications.

Fact 2

Adoption of cloud-hosted AI inference services brings familiar long-lived credential risk

To make cloud-hosted AI services easier to adopt, providers offer dedicated ways of using long-lived static credentials as a path of least resistance. But those keys are a valuable target: Criminals can steal them and resell access to third-party users, and model distillation gives them a further reason to go after credentials that open access to inference services.

As of September 2026, more than one in five organizations use cloud-hosted AI inference services such as Amazon Bedrock, Azure Foundry Tools, and Google Cloud’s Gemini Enterprise Agent Platform. Nearly half of organizations using Gemini use long-lived Gemini API keys, while only 17% of organizations using Amazon Bedrock use Bedrock API keys. In Azure, the pattern differs: Azure Foundry resources are by default created with long-lived keys already generated and able to be used for authentication; the vast majority of Azure organizations (97%) don’t change this behavior, meaning developers have access to long-lived keys that are already available.
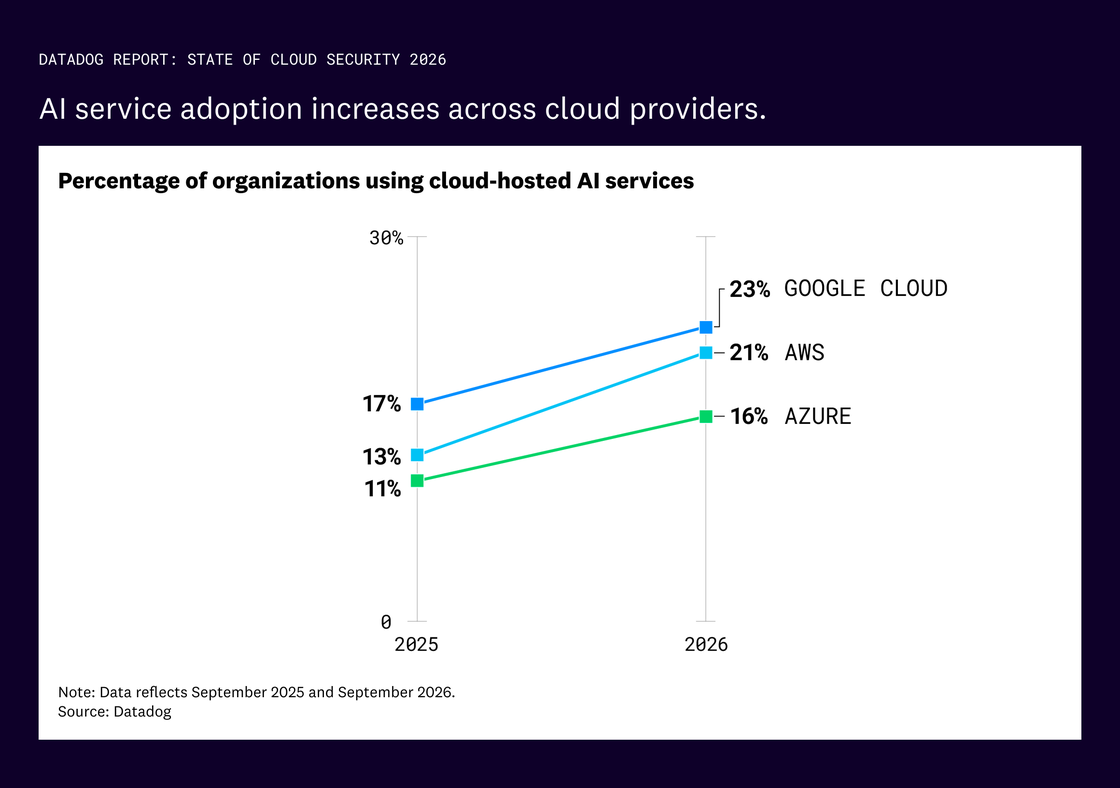
Slope chart titled Percentage of organizations using cloud-hosted AI services. Compares September 2025 and September 2026: Google Cloud rose from 17% to 23% of organizations, AWS from 13% to 21%, and Azure from 11% to 16%. Above the chart, a headline reads AI service adoption increases across cloud providers.

Rather than static Bedrock or Gemini API keys, you should access AI inference services through the calling workload’s short-lived identity when supported (IAM role, managed identity, or service account) so the model is reached with the same federated credentials as other cloud resources and not a separate long-lived key.

The choice between a convenient static key and a short-lived identity is the same decision every long-lived credential forces in the cloud. Long-lived credentials are one of the most common root causes of publicly documented cloud breaches year after year. Offensive tooling has long specialized in automating the finding of these flaws: Red-team frameworks like Pacu and Datadog’s own Pathrunner along with secret scanners like TruffleHog reliably find over-permissioned credentials and exposed keys at scale. That same tooling is available to autonomous attackers, who enumerate for long-lived credentials first because they’re the highest-value, longest-lived prize in the environment.

Across AWS, Azure, and Google Cloud, the legacy long-lived credential (the IAM user access key, the service account key) remains pervasive, old, and unused. We found that 43% of AWS IAM users, 41% of Google Cloud service accounts, and 66% of Entra ID app registrations have active keys created in the past year, and those keys then age into risk. The share of users with access keys older than three years has climbed steadily in AWS and Google Cloud since 2024, while only Azure has trended downward.
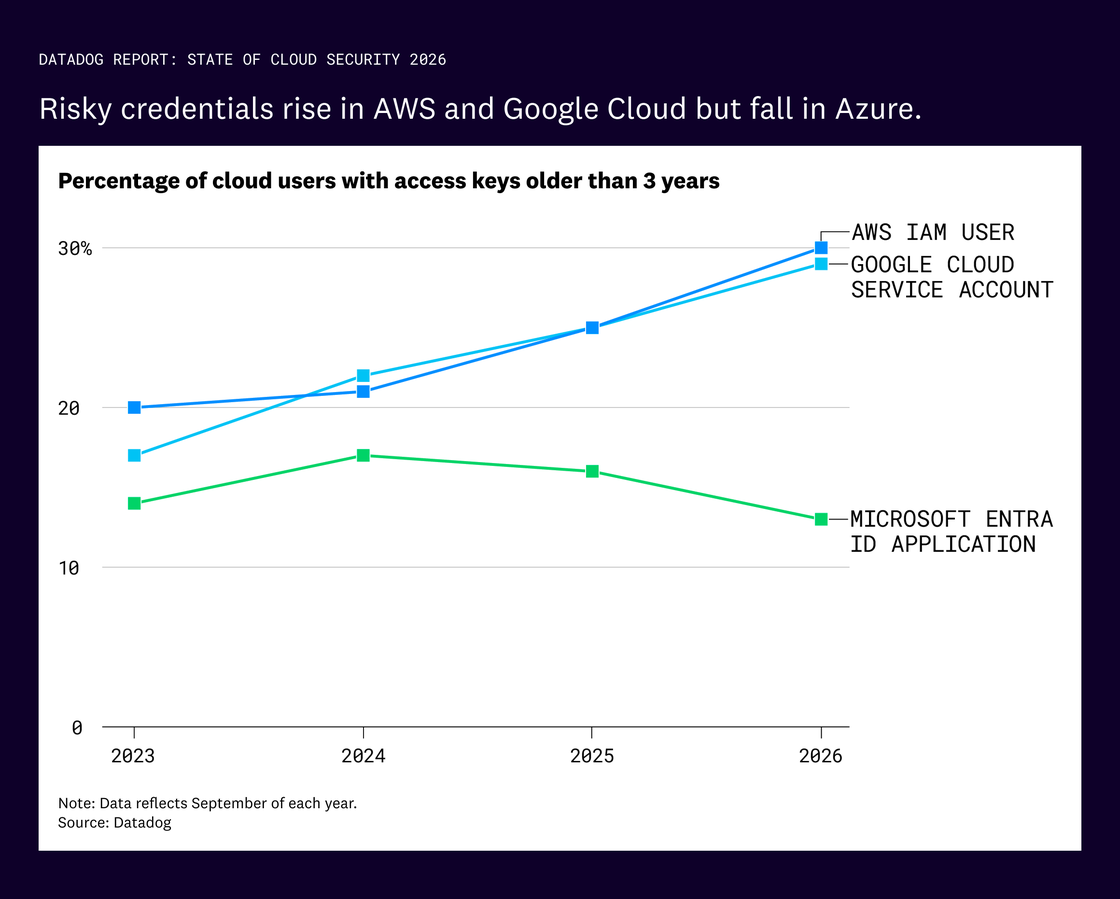
Line chart titled Percentage of cloud users with access keys older than 3 years. From 2023 to 2026, the share rises from 20% to 30% for AWS IAM users and from about 17% to 29% for Google Cloud service accounts, while Microsoft Entra ID applications peak at about 17% in 2024 and fall to about 13% in 2026. Above the chart, a headline reads Risky credentials rise in AWS and Google Cloud but fall in Azure.

Encouragingly, 63% of organizations exclusively use single sign-on (SSO) through AWS Identity Center and federated access, slightly up from 59% in 2025 and 55% in 2024. However, 37% of organizations still use long-lived credentials through IAM users accessing the AWS console, down slightly from 41% in 2025 and 45% in 2024. The rate of exclusive SSO adoption roughly matches the rate at which organizations remove long-lived credentials.
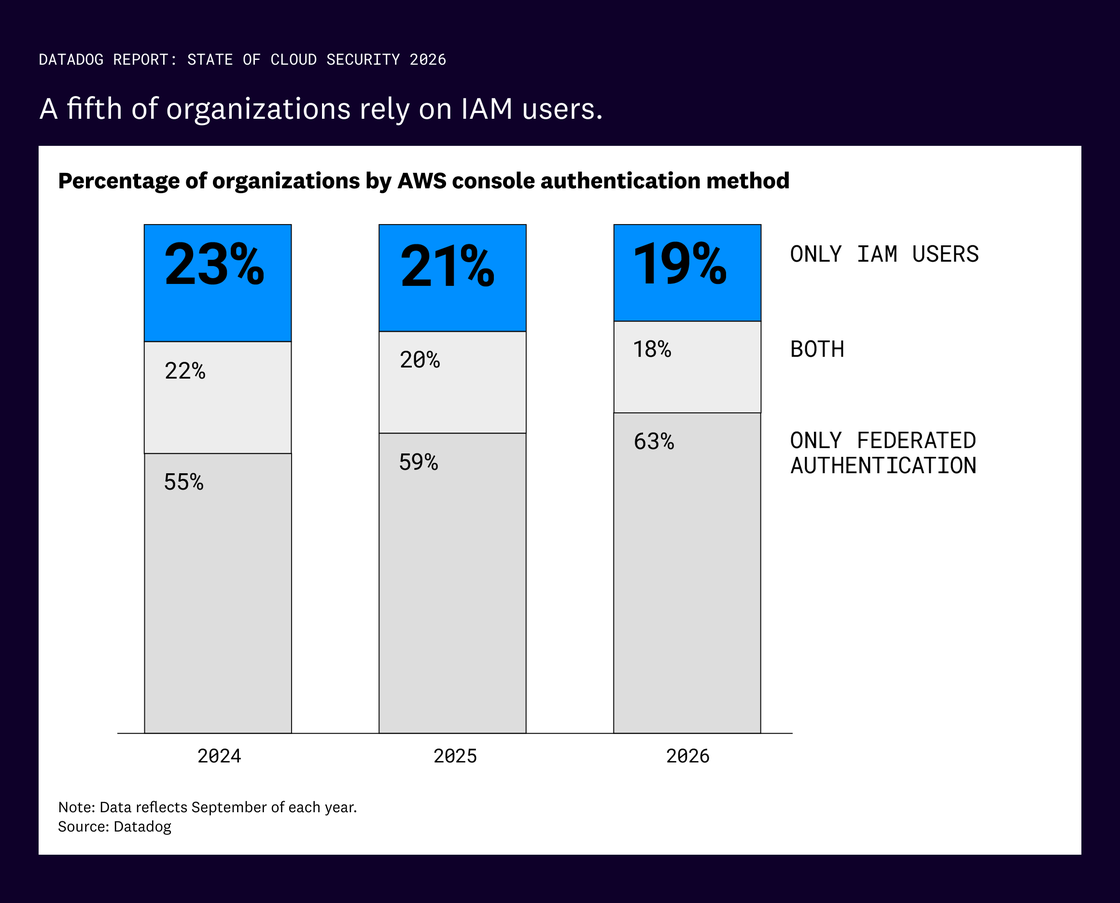
Stacked bar chart titled Percentage of organizations by AWS console authentication method. In 2024, 23% of organizations used only IAM users, 22% used both IAM users and federated authentication, and 55% used only federated authentication. In 2025, those numbers were 21%, 20%, and 59%, and in 2026, they were 19%, 18%, and 63%. Above the chart, a headline reads A fifth of organizations rely on IAM users.

Humans accessing cloud environments should use identity federation from centralized SSO and avoid using long-lived credentials such as IAM user access keys. Workloads that require cloud access should use platform-native authentication mechanisms that generate short-lived credentials, such as IAM roles for EC2 instances in AWS, managed identities in Azure, and service accounts attached to virtual machines in Google Cloud. Guardrails can then help prevent long-lived credentials from being created unintentionally, for example, by using the disableServiceAccountKeyCreation organization constraint in Google Cloud or by deploying a service control policy (SCP) in AWS that blocks actions such as iam:CreateAccessKey.

Fact 3

Supply-chain malware is adding cloud-specific attack mechanisms

Supply-chain attacks increasingly run autonomously and at machine speed. In 2026, a bot calling itself hackerbot-claw spent 10 days probing major open source projects (Datadog’s own among them) for vulnerable GitHub Actions workflows. The bot landed code execution in most of its targets and a full repository takeover in one. These cloud environment attacks travel well-trodden paths—a hijacked dependency propagating from developer laptops to CI/CD pipelines to production—but they’re much faster and carry cloud-specific payloads.

New dependency versions reach cloud applications quickly: 60% of organizations we analyzed run versions that were released less than 24 hours earlier. These versions appear in more than one in five (21%) cloud applications. This matters because supply-chain malware such as Shai-Hulud targets not only the application, but also cloud credentials and services.
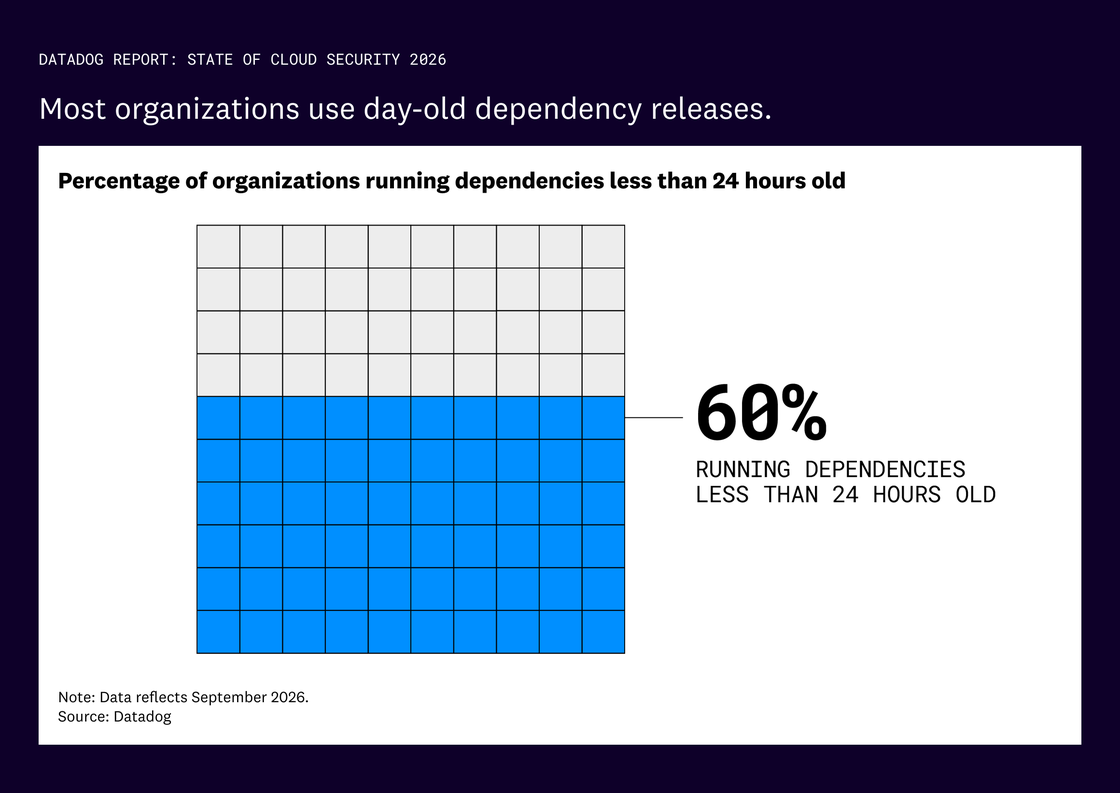
Waffle chart titled Percentage of organizations running dependencies less than 24 hours old. Shows that 60% of organizations run dependency versions that were released less than 24 hours earlier. Above the chart, a headline reads Most organizations use day-old dependency releases.

We found that application workloads running in cloud environments have 149 software dependencies on average (median: 129). Across an organization, cloud application workloads have 568 software dependencies on average (median: 362). We also found that more than half of these dependencies are transitive, limiting developers’ visibility into them. This number varies significantly depending on the ecosystem. Only 32% of NuGet (.NET) dependencies are transitive, compared with 86% of npm dependencies. We also found that applications running in cloud environments have more dependencies than applications running in other types of environments.
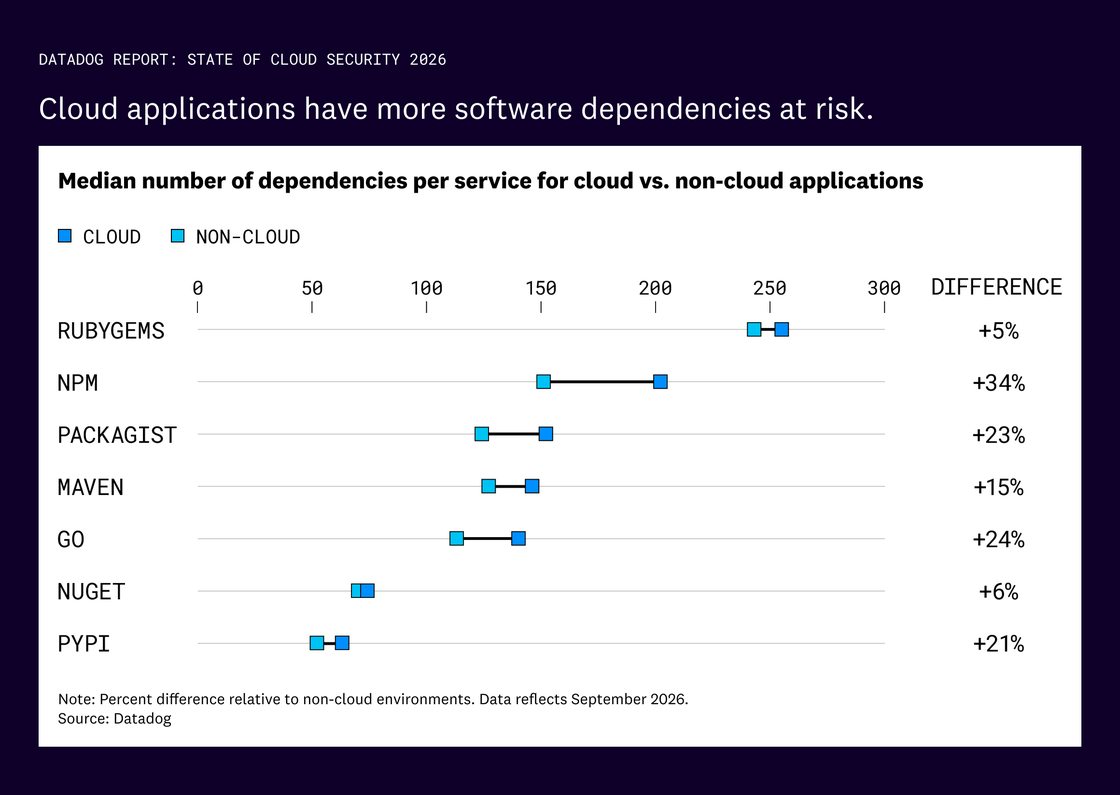
Dot plot titled Median number of dependencies per service for cloud vs. non-cloud applications. Shows that cloud applications have more dependencies than non-cloud applications in every ecosystem: RubyGems (+5%), npm (+34%), Packagist (+23%), Maven (+15%), Go (+24%), NuGet (+6%), and PyPI (+21%). Above the chart, a headline reads Cloud applications have more software dependencies at risk.

Supply-chain malware increasingly includes capabilities that target cloud credentials and cloud environments. Threats such as the Shai-Hulud malware family (whose source code was leaked) explicitly go after cloud credential files, secrets stored in cloud-based secrets managers, and short-lived credentials available in the instance metadata service. One variant, dubbed “Mini Shai-Hulud,” even includes cloud-specific code that deploys malicious payloads to cloud environments using the AWS Systems Manager (SSM) SendCommand API to execute commands on running EC2 instances.

This isn’t only theoretical: GitGuardian’s analysis of data leaked by the Shai-Hulud 2.0 campaign found hundreds of cloud credentials. Organizations should implement dependency cooldowns to lower the risk of malicious dependencies reaching their cloud environments, because the community usually identifies and contains hijacked libraries within a few hours.

Fact 4

Keyless authentication coexists with long-lived credentials in CI/CD pipelines

For CI/CD pipelines, long-lived credentials are also a core concern: Pipelines authenticate to the cloud constantly, usually hold broad deploy permissions, and are increasingly targeted through malicious software dependencies and code injection, seeking credentials to exfiltrate and use in subsequent attacks. Long-lived cloud credentials are challenging to rotate and are more likely to be leaked through a misconfiguration or vulnerability in the deployment pipeline.

The best practice is to use authentication based on OpenID Connect (OIDC) (also known as keyless authentication), allowing each pipeline to present a vetted identity to the cloud environment and retrieve credentials that are valid for only a short time.

In this context, we analyzed how organizations that use the popular CI/CD platform GitHub Actions authenticate their pipelines to AWS, Google Cloud, and Azure. We found that while OIDC usage is increasing year over year in AWS, its adoption remains uneven across providers. In AWS, 54% of organizations exclusively use keyless authentication for their GitHub Actions workflows (up from 45% in 2025 and 37% in 2024), compared with 22% in Google Cloud and 5% in Azure. Many organizations use OIDC-based authentication alongside other authentication methods (22% in AWS, 13% in Google Cloud, and 52% in Azure).
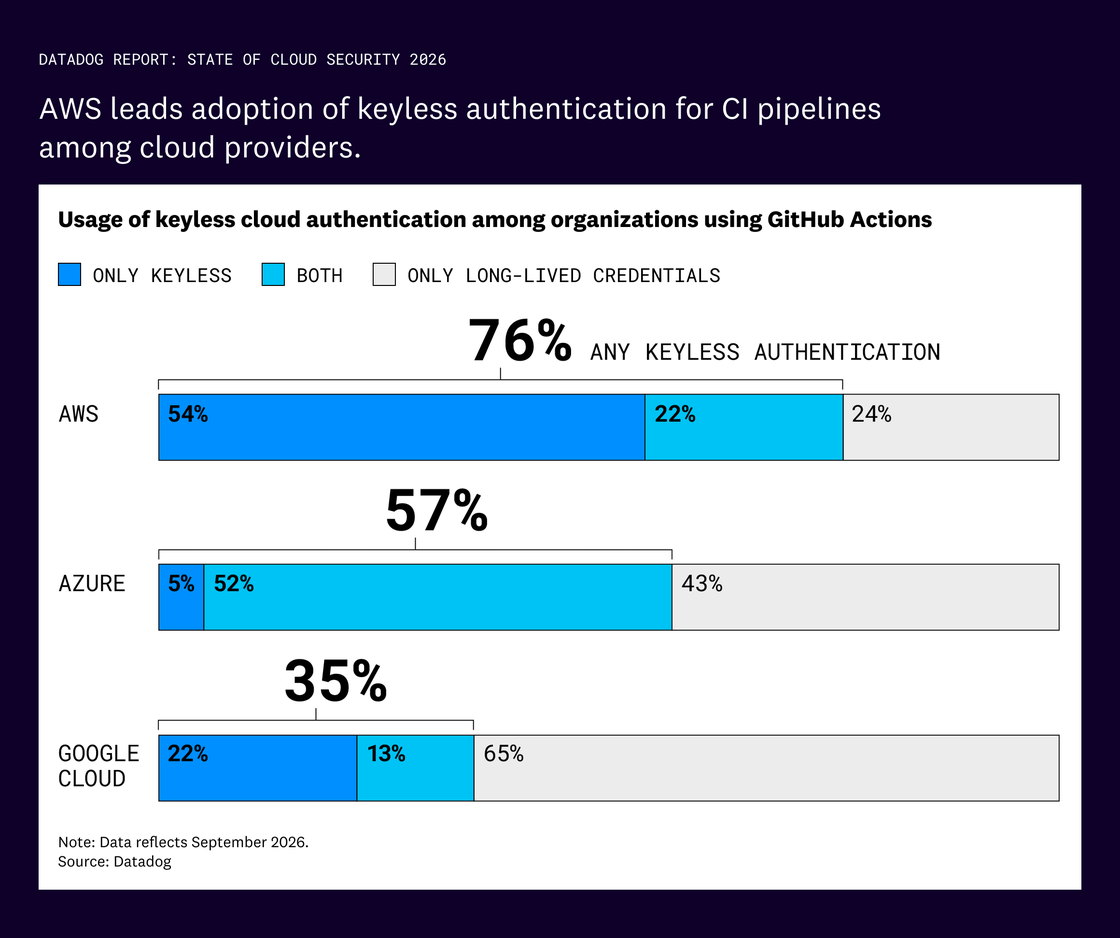
Stacked bar chart titled Usage of keyless cloud authentication among organizations using GitHub Actions. In AWS, 54% of organizations use only keyless authentication, 22% use both keyless authentication and long-lived credentials, and 24% use only long-lived credentials, for a total of 76% using any keyless authentication. In Azure, the split is 5%, 52%, and 43% (57% using any keyless authentication). In Google Cloud, it is 22%, 13%, and 65% (35% using any keyless authentication). Above the chart, a headline reads AWS leads adoption of keyless authentication for CI pipelines among cloud providers.

Organizations that use CI/CD pipelines to deploy infrastructure and applications to cloud environments should use keyless OIDC-based authentication, which is easier to deploy and scale and is more secure because it relies on short-lived credentials. This authentication mode is supported by all major CI/CD platforms, including GitHub Actions, CircleCI, GitLab CI/CD, Bitbucket, and Azure DevOps.

Fact 5

Data perimeters become common in AWS, while organization-level enforcement remains rare

Because cloud providers’ APIs are exposed to the internet by design, an attacker compromising cloud credentials can use them from anywhere in the world to access the cloud environment and data it contains. To mitigate this threat, data perimeters help ensure that access to cloud resources and data is allowed only if credentials are valid and have appropriate permissions, and the request originates from a trusted account or network.

The first step to implementing data perimeters is to use AWS Organizations with a multi-account strategy. We found that although 96% of organizations use AWS Organizations, only 55% of organizations implement data perimeters, up from 40% in 2025.

We analyzed how organizations implement data perimeters and found that most do so at the resource level. Of all organizations having at least one S3 bucket, VPC endpoint, SCP, or RCP, 47% use S3 bucket policies to implement them (through explicit deny and condition keys), compared with 19% that use a VPC endpoint policy. Few organizations use more scalable mechanisms such as SCPs and resource control policies (RCPs), which allow the creation of more effective data perimeters that span multiple AWS accounts.
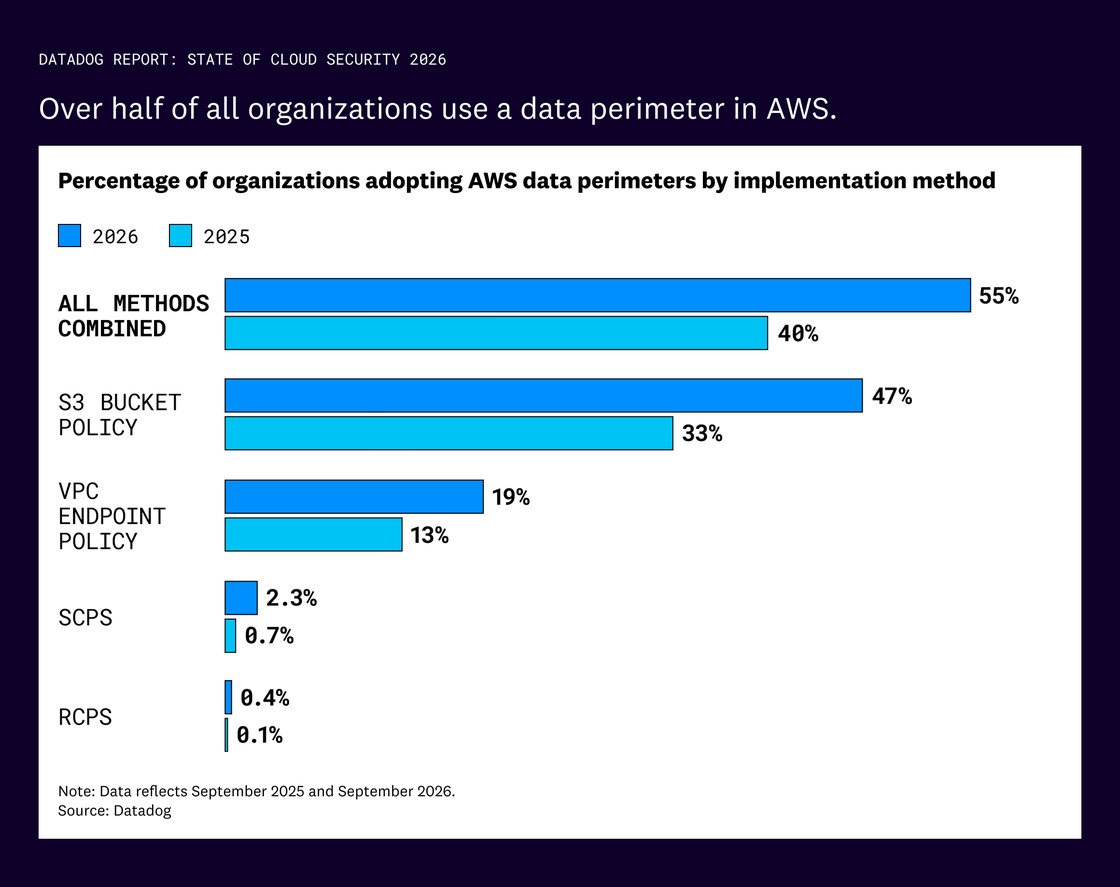
Bar chart titled Percentage of organizations adopting AWS data perimeters by implementation method. Compares 2025 and 2026: all methods combined rose from 40% to 55% of organizations, S3 bucket policies from 33% to 47%, VPC endpoint policies from 13% to 19%, SCPs from 0.7% to 2.3%, and RCPs from 0.1% to 0.4%. Above the chart, a headline reads Over half of all organizations use a data perimeter in AWS.

We also found that 14% of organizations run EC2 instances in their organization management account, up from 9% in 2025. In addition to not using the security controls offered to them by AWS Organizations, an increasingly large share of organizations create additional risk by running workloads in their organization’s management account. There, a single compromised workload can lead to the entire organization being compromised.

While organizations have the foundation to build efficient and scalable data perimeters, most rely on resource-specific data perimeters and don’t build on modern options that easily scale. Organizations should use a multi-AWS-account strategy with AWS Organizations and AWS IAM Identity Center for SSO, and they should implement data perimeters and security invariants by using SCPs and RCPs. To keep workloads out of the management account, they can delegate policy and service administration to member accounts.

Subscribe for more Datadog security research, events, and updates.

Subscribe to the Datadog Security Digest

Methodology

Findings are based on data collected in September 2026, unless otherwise noted.

Population

For this report, we analyzed the cloud security posture of a sample of thousands of organizations. Data in this report has come from customers of Datadog Infrastructure Monitoring, Datadog Logs, and Datadog Cloud Security.

Fact 1

We analyzed vulnerabilities in third-party libraries called by applications that use Datadog Code Security’s Software Composition Analysis feature.

We focus on open high and critical vulnerabilities only.

Fact 2

Cloud-hosted AI services

We define frameworks as libraries that manage agent state, tool execution, and control flow. We identified AI framework usage by looking at the dependencies in services with APM instrumentation.

We considered that a service was running in a cloud environment when its APM service configuration identified AWS, Azure, or Google Cloud as the hosting provider.

AI frameworks considered include OpenAI Agents, LangGraph, LangChain, Langflow, CrewAI, Microsoft AutoGen, LlamaIndex, CAMEL-AI, MetaGPT, smolagents, Flowise, SuperAGI, Griptape, n8n, Haystack, Spring AI, AgentScope, AgentFlow, Atomic Agents, OpenHands, Prompt Flow, Strands Agents, Letta, Rasa, Lindy, Vercel AI SDK, Botpress, Marvin, Instructor, Guidance, AWS Bedrock Agents, Pydantic AI, Microsoft Semantic Kernel, Mastra, and Chainlit.

AWS console authentication method

To identify the method used to authenticate the AWS console, we used CloudTrail events with the event type ConsoleLogin. Specifically, we considered that the authentication was performed through an IAM user for all events matching:

source:cloudtrail 
  AND @evt.name:ConsoleLogin 
  AND @userIdentity.arn:*user/*
  AND NOT @userIdentity.arn:*:root*

We considered that the authentication was performed through a federated identity provider for all events matching:

source:cloudtrail AND (
(@evt.name:ConsoleLogin @userIdentity.arn:*assumed-role/*)
  OR
  (source:cloudtrail @evt.name:ConsoleLogin 
@userIdentity.arn:*federated-user/*)
)

Long-lived credentials

For AWS, we considered IAM users that have at least one active access key. When an IAM user had several active access keys, we considered only the oldest one.

For Google Cloud, we considered service accounts that are not disabled and have at least one active access key. We excluded from our analysis Google-managed service accounts, for which it’s not possible to create user-managed access keys.

For Microsoft Entra ID, we considered Microsoft Entra ID app registrations that had active “password” credentials (corresponding to static access keys that can be exchanged for OAuth 2.0 access tokens).

Fact 3

For this fact, we used runtime telemetry for a large number of services and organizations that use Datadog Code Security.

For the first graph, we analyzed direct and transitive dependencies of each application, and filtered to retain only the ones using a version that was released 24 hours ago or less.

For the second graph, we considered that a service was running in a cloud environment when we had evidence it was running on AWS, Azure, or Google Cloud.

Fact 4

AWS

To identify organizations that use GitHub Actions with OIDC authentication on AWS, we queried AWS CloudTrail logs using the following Datadog logs query:

@eventName:AssumeRoleWithWebIdentity
@userIdentity.identityProvider:*token.actions.githubusercontent.com* -status:error

To identify organizations that use GitHub Actions with IAM users, we queried AWS CloudTrail logs using the following Datadog logs query:

@userIdentity.accessKeyId:AKIA* @userIdentity.type:IAMUser -status:error
source:cloudtrail AND @network.client.ip:* AND @userIdentity.accessKeyId:AKIA* AND @userIdentity.type:IAMUser AND -status:error

Google Cloud

For Google Cloud, we determined that GitHub Actions using OIDC authentication were the ones corresponding to the following logs query for Google Cloud Admin audit logs:

source:gcp.* @data.protoPayload.serviceName:sts.googleapis.com @data.protoPayload.methodName:google.identity.sts.v1.SecurityTokenService.ExchangeToken @data.protoPayload.authenticationInfo.principalSubject:repo\:* -status:error

Conversely, we identified cases where a GitHub Action authenticated to Google Cloud with static service account credentials using the following query:

source:gcp.* @data.protoPayload.authenticationInfo.serviceAccountKeyName:* @data.protoPayload.authenticationInfo.principalEmail:*gserviceaccount.com -status:error

Azure

For Azure, we determined that GitHub Actions using OIDC authentication were the ones corresponding to the following logs query in Entra ID activity logs:

source:azure.activedirectory @operationName:"Sign-in activity" @category:ServicePrincipalSignInLogs @properties.clientCredentialType:federatedIdentityCredential @resultType:0

Conversely, we identified cases where a GitHub Action authenticated to Azure with a long-lived key for an Entra ID app registration:

source:azure.activedirectory
  @operationName:"Sign-in activity"
  @category:ServicePrincipalSignInLogs
  @resultType:0
  (@properties.clientCredentialType:clientSecret OR @properties.clientCredentialType:clientAssertion)

Filtering on GitHub Actions source IP address

For all three cloud providers, we also filtered the results on source IPs known to be used by GitHub Actions, as determined by GitHub’s API endpoint.

Fact 5

We analyzed SCPs, RCPs, VPC endpoint policies, and S3 bucket policies and considered that they were using an AWS data perimeter when they contained any of the following AWS IAM condition keys in any of the statements:

aws:PrincipalAccount
aws:PrincipalOrgID
aws:PrincipalOrgPaths
aws:ResourceAccount
aws:ResourceOrgID
aws:ResourceOrgPaths
aws:SourceAccount
aws:SourceIp
aws:SourceOrgID
aws:SourceOrgPath
aws:SourceVpc
aws:SourceVpce

For this edition, we did take into account the condition keys aws:VpceAccount, aws:VpceOrgPaths, and aws:VpceOrgID, which were released in August 2025.

The ratio of organizations using SCPs, RCPs, VPC endpoints, or S3 bucket policies to implement a data perimeter was computed over the number of total organizations having at least one such SCP, RCP, VPC endpoint, or S3 bucket.

Licensing

Report: CC BY-ND 4.0

Images: CC BY-ND 4.0